
- Career Development
CSFR
Cyber Scheme Foundations: Risk
Understand, assess and manage cyber security risk with confidence.
A three-day practitioner course providing a practical introduction to cyber security risk management, combining expert-led instruction with exercises, individual activities and group-based scenarios.
at a glance
- Duration: Three days
- Timings: 09:30 to 17:00 each day
- Delivery: In person at The Cyber Scheme’s training centre in Cheltenham
- Dates: Please click the ‘book a course’ button above to access upcoming course dates
- Price: £995 +VAT to include the training course and associated assessment
- Assessment: End-of-course examination, 90 minutes, multiple choice and short-form written questions
- Qualification: CSFR (Cyber Scheme Foundations: Risk) certification and digital badge.
Why cyber risk management matters
Effective cyber security depends on organisations understanding what they are protecting, the threats they face, the vulnerabilities that may be exploited and the consequences if a risk materialises. Cyber risk professionals help organisations make informed decisions about where to focus effort, how to treat risk and how to communicate it clearly to the people responsible for business outcomes.
Cyber Scheme Foundations: Risk introduces the principles and practices that underpin this work. Participants move from the fundamentals of risk through to assessment, treatment, ownership, governance and the measurement of control effectiveness.
Why choose Cyber Scheme Foundations: Risk?
Cyber risk management sits at the heart of effective cyber security. Organisations need people who can identify and assess risk, understand business impact, support decision-making and communicate clearly with stakeholders. As cyber security teams become increasingly involved in governance, resilience, compliance and business risk, these skills are becoming essential across a wide range of roles.
Cyber Scheme Foundations: Risk has been designed to provide a practical introduction to the discipline. Combining expert-led instruction, discussion, knowledge checks, practical exercises and realistic scenarios, the course helps participants understand how cyber risk is identified, assessed, treated, governed, measured and communicated in real-world organisations.
Whether you are beginning a cyber risk career, supporting governance and compliance activities, or looking to strengthen your understanding of risk management, this course provides a structured foundation that can be applied immediately in the workplace.
WHAT YOU WILL LEARN
Cyber security risk management is about far more than maintaining a risk register. It requires an understanding of what an organisation is trying to protect, the threats it faces, how those threats could affect business objectives, and what action should be taken in response.
Learning is delivered through expert-led instruction, practical exercises, individual activities and group-based scenarios. A final risk-management exercise gives participants an opportunity to bring the course material together and apply it to a realistic situation.
Participants complete a 90-minute examination at the end of day three, comprising multiple-choice and short-form written questions. The assessment is designed to evaluate understanding of the course content and the ability to apply cyber risk management concepts in practice.
- Explain the fundamental principles of cyber security risk.
- Identify and analyse assets, threats and vulnerabilities
- Assess likelihood and impact using appropriate methodologies.
- Distinguish between inherent and residual risk.
- Determine whether risk sits within an organisation’s appetite and tolerance.
- Identify appropriate risk treatment options.
- Understand who should own and manage a risk.
- Apply recognised risk frameworks and methodologies.
- Evaluate the effectiveness of security controls.
- Develop meaningful risk metrics and indicators.
- Communicate risk to technical and non-technical stakeholders.
- Apply risk management principles to realistic cyber security situations.
PRACTICAL LEARNING
Learning is delivered through a blend of expert-led instruction, discussion, individual activities, knowledge checks and group-based scenarios.
Throughout the course, participants are encouraged to apply concepts to realistic organisational situations, helping them move beyond theory and develop practical judgement. The programme culminates in a final risk-management exercise that brings together the techniques, frameworks and principles covered during the course.
The emphasis throughout is on understanding how risk management works in practice and how it can be applied within real organisational environments.
PROFESSIONAL DEVELOPMENT
Cyber risk management is a growing and increasingly important discipline within the cyber security profession.
Alongside the core course content, participants will gain an understanding of professional responsibilities, ethical practice and the UK cyber security professional registration landscape. The course explores how cyber risk roles fit within the wider profession and helps participants understand potential development pathways within governance, risk and compliance disciplines.
MEET THE INSTRUCTOR
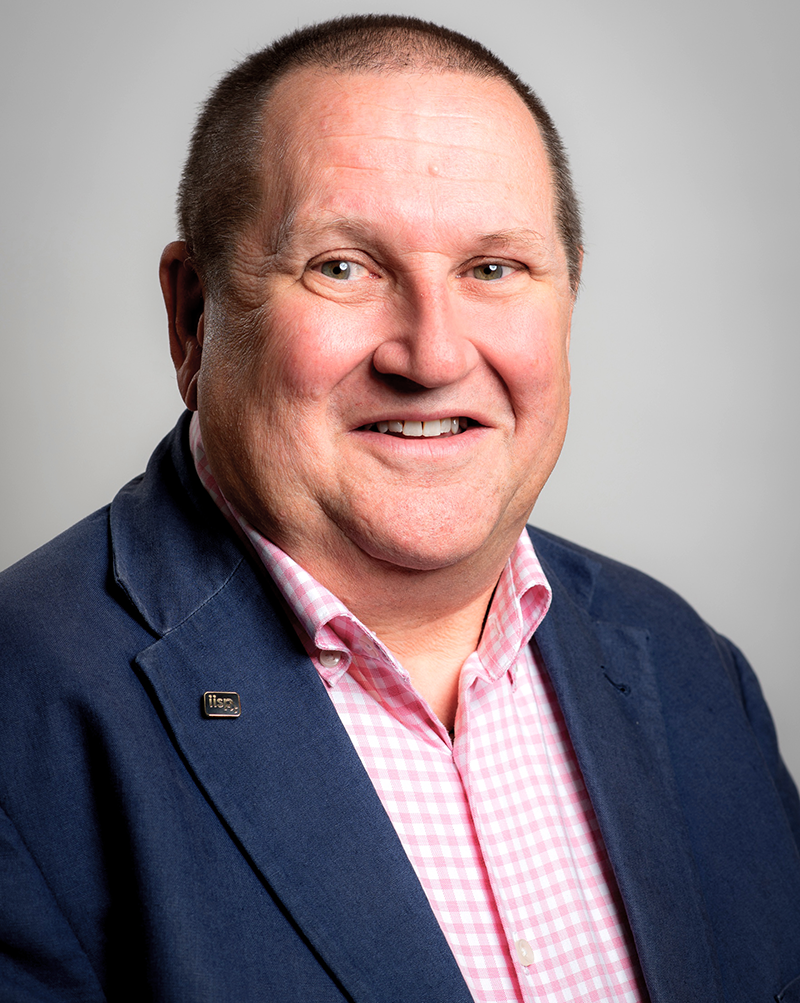
Peter Loomes has more than 35 years’ experience assessing organisational risk across healthcare, central government, industry and the charity sector. Throughout his career he has worked with organisations to understand risk, improve decision-making and develop practical, proportionate approaches to security.
As a Chartered Cyber Security Professional in Risk and Governance, Chartered Engineer, Chartered IT Professional and Fellow of the Chartered Institute of Information Security, Peter brings extensive professional experience alongside a pragmatic and accessible teaching style.
His approach focuses on making risk understandable, relevant and applicable to the real challenges organisations face. Rather than viewing risk as a compliance exercise, Peter helps participants understand how effective risk management supports better business outcomes and more informed security decisions.
Why we created this course…
"Cyber security isn't just about technology. Organisations need people who can understand risk, make informed decisions and communicate effectively with stakeholders. This course provides a practical foundation in cyber security risk management, helping participants build confidence, develop professional judgement and apply risk principles in real-world situations."
Zeshan Sattar, Director, The Cyber Scheme
WHO SHOULD ATTEND?
FAQs
This training has been independently reviewed through The Cyber Scheme’s Training Accreditation framework. Accreditation reviews course structure, delivery approach, learning outcomes and relevance to professional practice.
It is a three-day practitioner course providing a practical introduction to cyber security risk management. It covers the core concepts, processes and decisions involved in identifying, assessing, treating, owning, governing and communicating cyber risk.
The course is designed for people who want to enter or develop within cyber risk management, including career changers, junior risk and GRC practitioners, and cyber or IT professionals who need a structured grounding in risk.
The course is positioned as a foundation-level introduction. The available course information does not specify mandatory previous cyber risk experience. Any final prerequisite wording will be confirmed before publication
Participants cover the risk lifecycle, assets, threats, vulnerabilities, likelihood, impact, appetite, tolerance, residual risk, ownership, methodologies, controls, governance, compliance, frameworks, metrics and communication.
Yes. The course combines expert-led teaching with practical exercises, individual activities and group-based scenarios, including a final risk-management exercise.
Delegates should preferably bring a laptop and charger, or a tablet. The device can use a supported Windows, macOS or Linux operating system and must run a supported browser.
Yes. Please contact The Cyber Scheme before the course so that any access requirements or reasonable adjustments can be discussed.
Delegates will be asked to read the course scenarios before attending. The scenarios and joining instructions will be supplied before the course.